
Cyber resilience in vocational education: make execution demonstrable
From the NBA framework to daily operations. Start with one check, clear ownership and evidence of confirmed execution.

A policy document describes how you intend to work. An audit also asks whether that happens in practice, who checks it and what follows when the outcome differs. For education institutions, these questions offer a practical starting point. You can begin with one check of existing data before changing operational processes.
Cyber resilience requires more than a score
MBO Digitaal emphasises demonstrable maturity and independent assessment in the Dutch vocational education Cyberweerbaarheidspool. Its sector benchmark also identifies room for improvement in execution. This makes the connection between policy, daily IT operations and evidence important. A technically successful import does not demonstrate that a control consistently works.
Consider an assigned laptop whose security status is missing, or a former employee who still has equipment recorded against their name. The question goes beyond differences between records. You need to know who reviews the discrepancy, what action follows and how completion is recorded.
Start with one check your team recognises
Choose a bounded question with security, application management and the process owner. For example: which active laptops in the asset register can be matched to the agreed security source? First define the population, the authoritative source for each field and the required freshness of observations.
- Make the agreement specific. Record the objective, scope, exceptions, owner and review frequency.
- Compare available data. Start with read-only access or a controlled export if appropriate. Keep uncertain matches visible.
- Have discrepancies reviewed. A missing observation can also result from an offline device, restricted permissions or an integration failure.
- Retain the outcome. Record what was investigated, the decision taken, who acted and when execution was confirmed.
- Repeat the check. A snapshot is a starting point. Repeated checks help establish whether the process continues to work.
GRC and execution each have a role
A GRC application supports records of risks, controls, assessments and evidence. Service management, identity and asset records support daily work. Service Automation Suite can connect data and configured follow-up actions between those environments, reducing repeated checks in disconnected spreadsheets.
Use existing integrations where they already address the need. For additional exchange, agree which data is available, who may receive it and how the original work remains traceable. TrustBound provides its own integrations and reporting. Build on that foundation to connect relevant data with work references and confirmed outcomes, keeping assessment and execution together.
A check is not a formal assurance statement
The mapping to the NBA information security maturity model requires substantive review by the responsible professionals and, where necessary, the independent auditor. They determine relevant statements and required evidence. Service Automation Suite does not assign an automatic NBA score or guarantee participation in the Cyberweerbaarheidspool.
It can help make a practical chain visible: the applicable agreement, the data used, the discrepancy reviewed and the confirmed outcome. That supports a grounded conversation between security, compliance, architecture and operations.
A small next step
We welcome a conversation about one check that fits your daily work. We agree access, data use, effort and the desired outcome beforehand. After reviewing the first findings, you decide whether and which follow-up actions to configure.
We would be pleased to hear from you. Explore education solutions and the possibilities around TrustBound GRC.
Further context: the Cyberweerbaarheidspool at MBO Digitaal and the sector benchmark. Always check current sector agreements for applicable conditions and frameworks.
Keep reading
Defender and your asset register: start with a read-only check · Digital autonomy: a practical next step together
More from the same context.
Defender and your asset register: start with a read-only check
Which registered devices appear in the security source? Connect observations, ownership and review before automating actions.
5 Nov 2026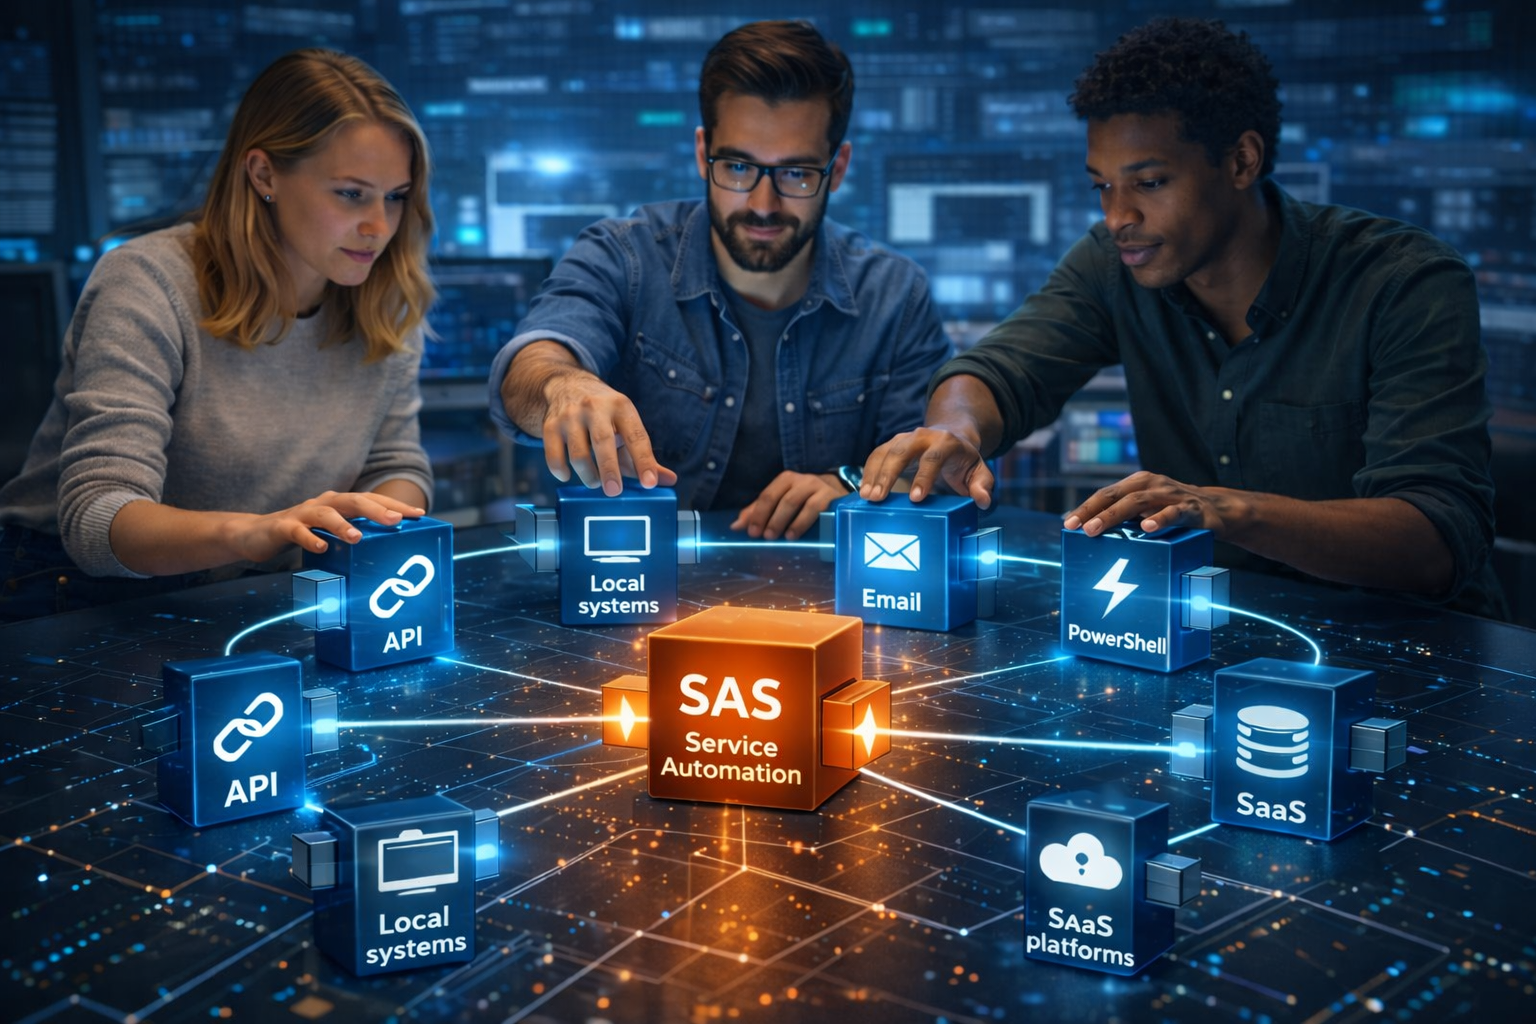
Digital autonomy: a practical next step together
Control over data, processes and change. We welcome conversations and collaboration with organisations working on these questions.
5 Nov 2026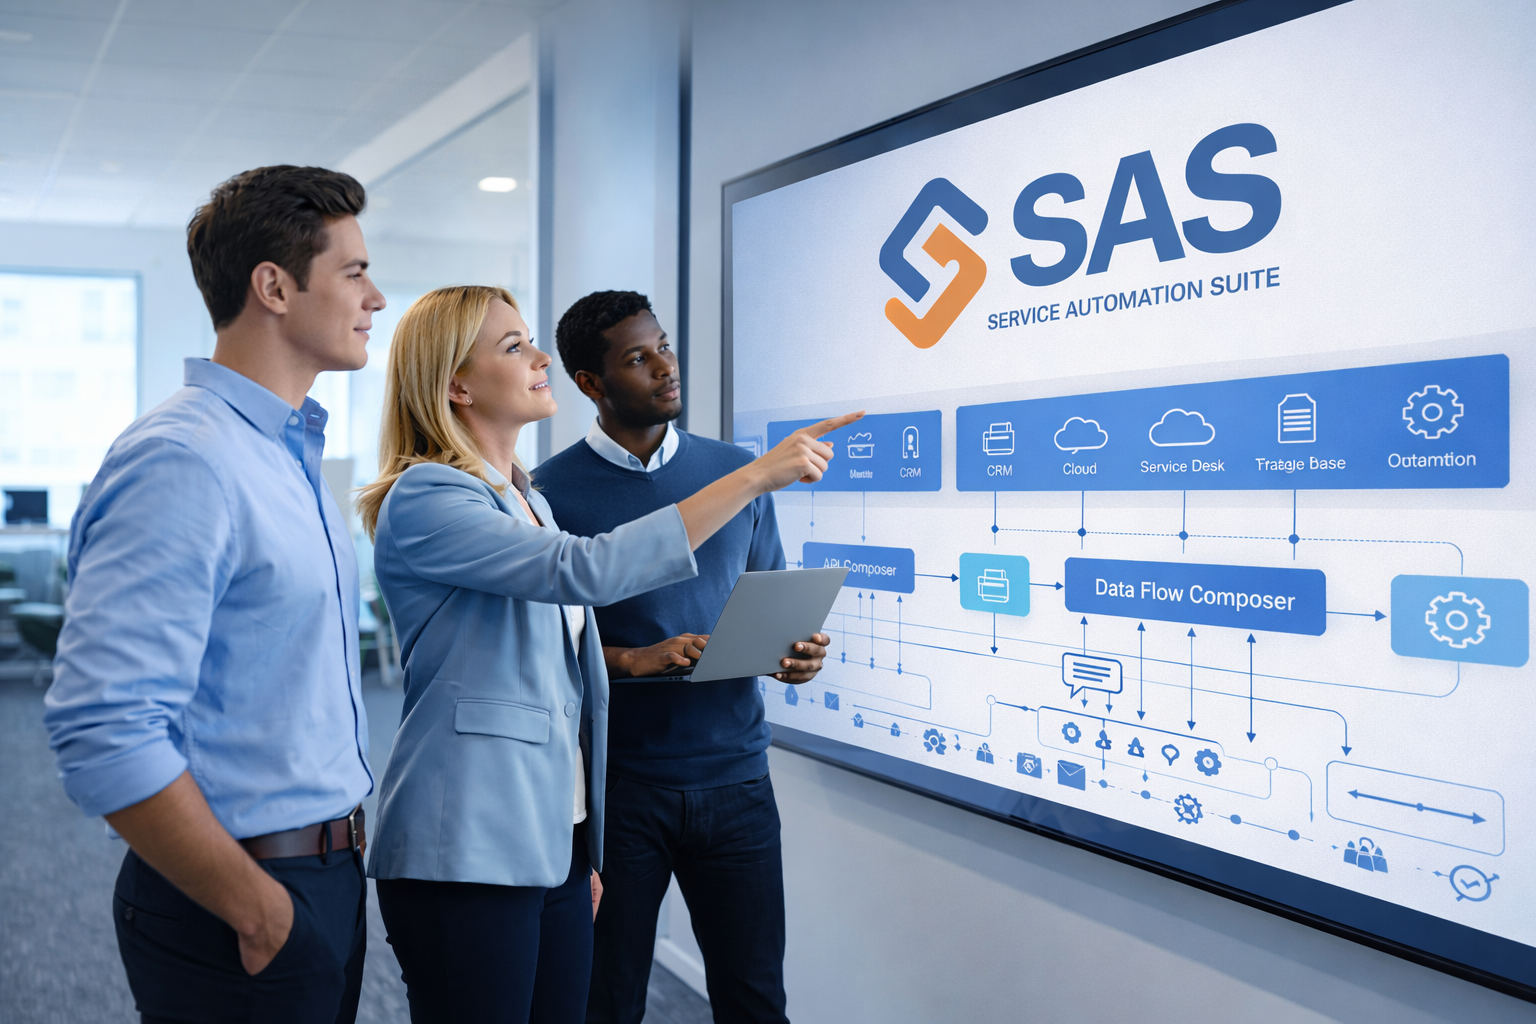
Digital autonomy requires control. Why we support the VNG’s direction.
Retain freedom of choice over processes, data and technology. Why Scope4mation supports the VNG’s attention to digital autonomy and wants to contribute with customers and partners.
Your ticket is with the supplier. What happens next?
From correct customer and device data to updates and exception handling: how we configure collaboration between your service desk and its suppliers with Service Automation Suite.
5 Nov 2026