
Defender and your asset register: start with a read-only check
Which registered devices appear in the security source? Connect observations, ownership and review before automating actions.

The laptop is in your records. But is it also visible to the agreed security tooling? If not, who investigates the difference? This is a concrete way to connect asset management and security without immediately changing devices or access rights.
Defender and asset records tell different stories
Microsoft Defender for Endpoint provides device observations and security context. Asset records describe matters such as agreed assignment and lifecycle. HR or a student information system can provide additional context. None of these sources alone proves that the entire equipment process is correct.
A device missing from the selected Defender data may be outside scope, insufficiently recent or invisible under the permissions used. “Not found” should therefore become an investigation question rather than an automatic conclusion that the device is unsafe, lost or returned.
A first comparison in four steps
- Define the population. Choose, for example, one managed laptop group. Agree how stock, classrooms, shared devices and exceptions are treated.
- Read the required data. Use only the necessary read permissions or a controlled export. Record retrieval times and whether retrieval completed successfully.
- Match the same device. Retain the relevant identifier from each source. Use only available, verified matching fields. A username or changing device name is not a reliable key on its own.
- Have differences reviewed. Give missing records, missing security observations and uncertain matches their own clear category, owner and expected follow-up.
How can Service Automation Suite contribute?
Using the existing API and data building blocks, we can read selected sources, establish relationships and run the agreed check. The initial result can be a review overview. Only afterwards, if desired, do we configure a service task, incident or targeted record correction.
We separate source failures from substantive discrepancies. If an API is unavailable, an empty result set cannot be taken as proof that no devices exist. We also define how repeated observations stay with the same investigation, avoiding a new ticket on every check.
A service ticket is not a resolved threat
Microsoft Defender and, where used, Microsoft Sentinel remain part of security operations. A service ticket supports agreed execution but does not automatically close the security incident. Tasks, ownership and feedback must fit the procedures of the security team or its service provider.
Isolating or wiping devices, excluding them from assessment or blocking accounts is outside this initial read-only check. Such actions require a separately reviewed configuration with appropriate permissions and responsibilities. Available current fields and incident data also depend on product, licence and environment.
What result can the team discuss?
A useful first outcome contains the selected population, sources, observation times, established relationships, uncertain cases and reviewed discrepancies. It also shows what still needs investigation and who owns it. You can then identify where automation helps and where human review remains necessary.
Microsoft documents read-only access to device fields through the Defender API. Observations remain subject to the configured retention period, and the portal and API can refresh at different times. These boundaries form part of the check definition.
We welcome a conversation about a suitable first check. Explore Microsoft Defender, Microsoft Sentinel and TOPdesk.
Technical context: Defender for Endpoint: List machines and device inventory and data freshness.
Keep reading
Cyber resilience in vocational education: make execution demonstrable · Digital autonomy: a practical next step together
More from the same context.
Cyber resilience in vocational education: make execution demonstrable
From the NBA framework to daily operations. Start with one check, clear ownership and evidence of confirmed execution.
5 Nov 2026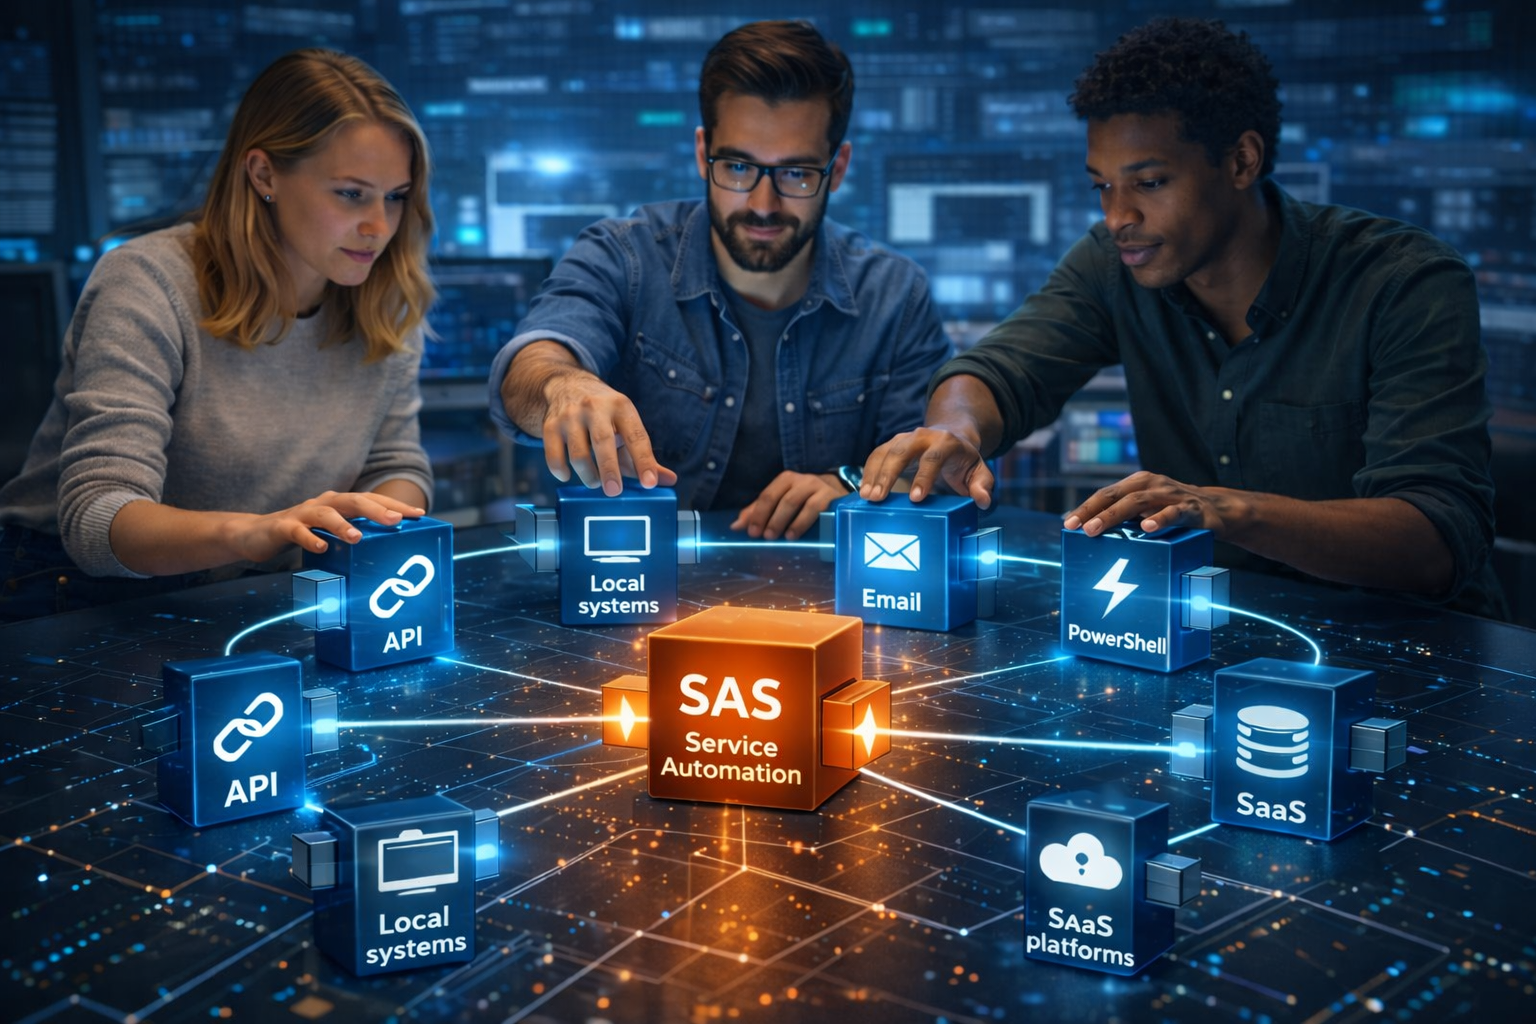
Digital autonomy: a practical next step together
Control over data, processes and change. We welcome conversations and collaboration with organisations working on these questions.
5 Nov 2026
Different laptop names in TOPdesk and Intune? Connect the right device.
Connect asset records and managed devices without duplicate administration. Understand identifiers, naming and controlled follow-up.
Your ticket is with the supplier. What happens next?
From correct customer and device data to updates and exception handling: how we configure collaboration between your service desk and its suppliers with Service Automation Suite.
5 Nov 2026